
Bring Your Own Cloud on GCP
This page covers running Akka Automated Operations (AAO) on GCP. For the architecture and concepts, start with the technical overview.
|
Download BYOC on GCP as a PDF, or the full overview. |
The architecture Akka provisions into your GCP project, with a VPC network, GKE, Cloud SQL, and the supporting services below.
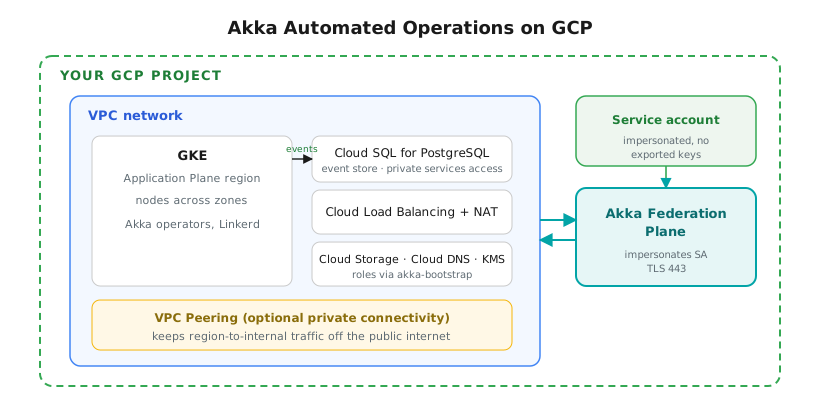
GCP resources
AAO on GCP uses these Google Cloud services (from the akka-bootstrap modules/google module):
-
Cloud IAM and Cloud Resource Manager (service account, custom roles, and bindings)
-
Compute Engine networking (VPC, subnets, Cloud NAT, external IP, Cloud Load Balancing)
-
Google Kubernetes Engine (GKE)
-
Cloud SQL for PostgreSQL
-
Service Networking (private services access for the database)
-
Cloud DNS (public and private zones)
-
Cloud KMS
-
Cloud Storage
Identity model
The cloud account is a GCP project. A dedicated Google service account is created for the region and assigned a non-human privileged role with the minimum permissions to set up and manage it. The service account is then configured so the Federation Plane’s identity can impersonate it to bootstrap and manage the region.
Rather than long-lived exported keys, the Federation Plane impersonates the dedicated service account, which keeps bootstrap and management credential-free on your side.
AAO uses four roles: Deployment (created by akka-bootstrap), and Editor, Viewer, and SRE (created by you). The exact roles and bindings are created and managed by akka-bootstrap and are the source of truth; review the generated permission reference rather than a copy here.
Google GKE
Managed Kubernetes hosts the Application Plane, with instances spread topologically across zones. The event store is Cloud SQL for PostgreSQL.
Installation
Prepare your project with the akka-bootstrap utility. In values.hcl, use a gcs backend and populate the gcp block of akka_regions, then run terragrunt init, terragrunt plan, and terragrunt apply. After a successful apply, share the generated service-account details with Akka so the Federation Plane can impersonate it. Bootstrap is driven by the modules/google Terraform module.
Private connectivity
By default, traffic between the region and your internal networks traverses the internet. To keep it private, AAO on GCP uses VPC Peering between the region VPC and your internal networks. The per-flow detail is on the data flows page.
Bringing your own GKE cluster (BYOK8s)
If you provision the cluster yourself, see Akka Automated Operations on GCP with your own Kubernetes for the complete, self-contained guide.